
The Cyberpolycrisis report
Report edition: 22 October 2026 · PDF page 1
A report for people responsible for keeping a business trading when software, suppliers and trust fail together. Read the research, work through the operating exercises, and turn the findings into a practical plan.
The expanded edition adds ten detailed reports under each of the original 26 topics. Explore six audience perspectives, evidence, business costs, technical exposure and recovery. The two later issue records and the complete PDF remain available.
Read the report, section by section.
375 linked pages · 260 detailed reports · Six audience perspectives · All 31 PDF pages covered.
Briefing
- Executive updateA briefing for technology and operations leaders managing overlapping supplier, software, identity and continuity risks. This revision retains the original 26 topics and adds AOMEI update-delivery research and GitLab's c
- What changed in this revisionBriefing
- PHP and GitLabPHP and GitLab. PHP exploitation attempts increase patch urgency. GitLab adds a critical unauthenticated code-execution patch. See issues 01 and 28.
- AI and supplier identitiesAI and supplier identities. Microsoft links ARTEX-assisted operations to the ConnectWise compromise; review downstream application persistence. See issue 22.
- LiteLLMLiteLLM. Vendor containment, registry-specific exposure windows and a recovery warning: running Python or pip can retrigger the payload. See issue 10.
- RailwayRailway. Partial service restoration replaces the initial deployment pause. Older API tokens are invalidated; downstream secret rotation remains necessary. See issue 17.
- ZeaburZeabur. The vendor reports account and environment-variable exposure and a phased December shutdown. Migration planning is now time-sensitive. See issue 18.
- Connected sites and trust storesConnected sites and trust stores. TeamUpdraft expands site checks to unexpected editors. eMudhra remediation includes explicit Cloudflare client and tunnel versions. See issues 06, 21 and 26.
- AOMEIAOMEI. Newly included research covers an earlier April-July campaign. Endpoint persistence can survive the vendor's repair. See issue 27.
- How to read this reportNews dates and incident dates differ. Vendor status is a dated snapshot, not a live availability guarantee. Confirmed incidents, vulnerabilities, research and policy are labelled separately. The collection does not estab
Issue register
- Issue registerUse the numbered entries for impact, potential exposure, required actions and linked primary evidence. Operational priority is conditional on your environment being affected.Priority guide. Critical means act now if expo
- Issue index 01 to 14Use the numbered entries for impact, potential exposure, required actions and linked primary evidence. Operational priority is conditional on your environment being affected.Priority guide. Critical means act now if expo
- Issue index 15 to 28Use the numbered entries for impact, potential exposure, required actions and linked primary evidence. Operational priority is conditional on your environment being affected.Priority guide. Critical means act now if expo
- Runtime and infrastructureRead the individual entries for impact, potential exposure, required actions and primary evidence. Operational priority depends on actual exposure.
- 01PHP critical remote code executionCritical · Patches; observed attack traffic
- PHP: Evidence and scopeA vulnerable installation is not evidence that its customer records were accessed. Market share cannot establish an affected-user count.
- PHP: Business impact and costsA shutdown can stop orders while a rushed restoration can reintroduce an unsafe runtime. Assess both the interruption to selling and the investigation required if an exposed service could reach customer or payment-related records.
- PHP: Technical exposure and controlsMap public hostnames to the actual executing runtime, including containers, appliances, hosting control panels and background workers. Record the owner and patch authority for each deployment.
- PHP: Response and recoveryReopen only when the runtime remediation is verified, critical trading tests pass, and the incident owner has decided whether further investigation is required.
- PHP: Business manager reportWhich customer promise becomes impossible if this service stays restricted for another business day?
- PHP: Business owner reportWho can prove that every internet-facing PHP service has an accountable maintenance path?
- PHP: Technical manager reportWhat evidence would reveal a second, forgotten installation after the first one is fixed?
- PHP: Software engineer reportCould rollback restore the vulnerable runtime, and what safer recovery option exists?
- PHP: Customer service reportCan a customer tell whether to wait, retry later or contact support about an existing order?
- PHP: Customer reportIs there a confirmed action for my account, or is this a general service update?
- 02Google Cloud London outage and banking disruptionHigh · Confirmed power outage
- Google Cloud: Evidence and scopeRegional service scope does not identify every affected bank or customer. A provider’s incident end time is not proof that an individual business has cleared its transaction backlog.
- Google Cloud: Business impact and costsInterruption can produce a delayed rather than permanently lost transaction. Count backlog, duplicate retries, missed settlement windows and manual reconciliation separately; otherwise a revenue-loss estimate can overstate or understate the real effect.
- Google Cloud: Technical exposure and controlsTrace both the application’s data path and its recovery dependencies: database, queue, DNS, identity, backup, monitoring and operator access. A different availability zone is not automatically an independent operating path.
- Google Cloud: Response and recoveryReturn to normal operations after service health, data consistency and backlog handling have been verified by the business and technical owners.
- Google Cloud: Business manager reportCan the team distinguish an unprocessed request from a completed request whose confirmation was delayed?
- Google Cloud: Business owner reportWhat business function can we still deliver when our normal regional control plane is unavailable?
- Google Cloud: Technical manager reportWhich supposedly independent recovery component still requires the failed region?
- Google Cloud: Software engineer reportDoes our retry logic preserve the business meaning of an operation after an ambiguous timeout?
- Google Cloud: Customer service reportCan we give an update without inventing a restoration time the provider has not committed to?
- Google Cloud: Customer reportIs the service still unavailable, or is my earlier transaction waiting for reconciliation?
- AI operations and procurementRead the individual entries for impact, potential exposure, required actions and primary evidence. Operational priority depends on actual exposure.
- 03Cairn: AI-assisted cybercrime operationsHigh · Researcher observations
- Cairn: Evidence and scopeThis is researcher-observed activity. It does not establish that every autonomous task succeeded or that all events in the report share one operator.
- Cairn: Business impact and costsAutomation can compress the time available to investigate a weak signal. The operational issue is whether the business can recognise and interrupt suspicious access before it spreads into systems that support trading.
- Cairn: Technical exposure and controlsReview reachable services and what their credentials can access. Model the interval between detection and revocation rather than assuming a human attacker will move slowly between steps.
- Cairn: Response and recoveryConsider the response exercise complete when the team can show an observed signal leading to an authorised containment decision and a verified business fallback.
- Cairn: Business manager reportWho can accept the operational consequences of revoking a critical integration tonight?
- Cairn: Business owner reportHow long would a credible alert wait for someone with authority to act?
- Cairn: Technical manager reportCan an alert owner find the system and credential owners without reconstructing the organisation chart?
- Cairn: Software engineer reportWhat can this workload still do after its primary key has been revoked?
- Cairn: Customer service reportWhich reports need urgent escalation rather than a standard service-delay reply?
- Cairn: Customer reportWhat evidence connects this notification to my account and the real service provider?
- 04DeepSeek restrictions in US federal civilian systemsHigh* · Official government order
- DeepSeek: Evidence and scopeDo not infer a universal private-sector ban or a contractor-specific legal conclusion from the notice. Applicability depends on the order, contracts, implementation and authorised interpretation.
- DeepSeek: Business impact and costsAn unplanned model removal can interrupt customer service or change output quality. The business problem is satisfying applicable obligations while maintaining a tested workflow and an auditable supplier inventory.
- DeepSeek: Technical exposure and controlsInventory model providers behind direct accounts, gateways, embedded assistants and subcontractors. Distinguish the visible product name from its configured underlying model and data route.
- DeepSeek: Response and recoveryResume the affected workflow when the authorised policy owner accepts the implementation evidence and business testing shows the replacement is usable.
- DeepSeek: Business manager reportCan the team deliver the same customer obligation while the tool is being assessed?
- DeepSeek: Business owner reportDo we know the providers behind the services we promise customers are approved?
- DeepSeek: Technical manager reportCould an automatic fallback send requests to a provider excluded by the applicable policy?
- DeepSeek: Software engineer reportDoes the replacement preserve access boundaries and business quality under degraded conditions?
- DeepSeek: Customer service reportWhat can we confidently say about the tool’s provider and where customer information goes?
- DeepSeek: Customer reportDoes this change affect the service I receive or an obligation in our agreement?
- Agent governance and certificate trustRead the individual entries for impact, potential exposure, required actions and primary evidence. Operational priority depends on actual exposure.
- 05Microsoft: AI agents as an insider-risk categoryHigh* · Vendor guidance
- AI agents: Evidence and scopeModel behavior and business authority are different layers. Monitoring or a second model cannot by itself prove that a consequential action is authorised.
- AI agents: Business impact and costsAn agent can perform a technically permitted action that is commercially wrong. Repeated refunds, unintended exports or incorrect promises can accumulate before staff notice a plausible-looking explanation.
- AI agents: Technical exposure and controlsList each agent’s tools, identity, data access, spending scope and approval path. Include scheduled agents and connections that survive beyond the employee session that created them.
- AI agents: Response and recoveryAllow production actions only within a documented scope that has passed denial, approval and recovery tests.
- AI agents: Business manager reportWhich actions create an obligation we cannot easily reverse?
- AI agents: Business owner reportWho remains responsible when an agent performs a permitted action with a bad business outcome?
- AI agents: Technical manager reportCan we stop one agent without disabling the entire customer operation?
- AI agents: Software engineer reportDoes the backend reject an unauthorised action even if the model confidently requests it?
- AI agents: Customer service reportDid the system merely suggest this remedy, or has it already executed it?
- AI agents: Customer reportCan a responsible person review this decision and explain what actually changed?
- 06eMudhra intermediate certificate compromiseCritical* · Confirmed trust incident
- eMudhra: Evidence and scopeThe ability to forge a trusted certificate does not prove interception of every connection. Cloudflare’s statement about its own observations is not clearance for customer-managed applications.
- eMudhra: Business impact and costsIncorrect trust can undermine the confidence placed in encrypted connections. Remediation can also cause legitimate integrations to fail, so the business must plan controlled updates without instructing staff to bypass certificate checks.
- eMudhra: Technical exposure and controlsIdentify the verifier for each important connection: operating-system store, language runtime, container bundle, proxy or custom mutual-TLS configuration. Record which updates become active only after restart or redeployment.
- eMudhra: Response and recoveryComplete the change only when every relevant verifier has evidence of remediation and service owners have accepted any integration exceptions.
- eMudhra: Business manager reportWhich customer commitment depends on a connection nobody has tested after the trust update?
- eMudhra: Business owner reportCan we explain which parts our providers fixed and which parts we still operate?
- eMudhra: Technical manager reportWhere could an old embedded trust store survive the operating-system update?
- eMudhra: Software engineer reportDoes a custom CA setting override the store we believe we patched?
- eMudhra: Customer service reportAre we asking the customer to fix something that actually belongs to our application?
- eMudhra: Customer reportIs this an official update, or a request to change which certificates my device trusts?
- AI service credentialsRead the individual entries for impact, potential exposure, required actions and primary evidence. Operational priority depends on actual exposure.
- 07OpenCode Console breach and linked AI accountsCritical* · Vendor-confirmed breach
- OpenCode: Evidence and scopeProduct documentation explains the credential relationship; it does not verify the incident, affected accounts or reimbursement eligibility.
- OpenCode: Business impact and costsThe business may face unexpected inference spending and uncertainty about how a shared key was used. Developer interruption and investigation effort should be tracked separately from any disputed charges.
- OpenCode: Technical exposure and controlsInventory the provider accounts connected to the console, which keys were shared, the scopes available to each, and the independent billing and audit views at the provider.
- OpenCode: Response and recoveryRestore the integration when its owner accepts the current vendor guidance and the business can observe and limit the new credential’s use.
- OpenCode: Business manager reportWhich team can keep working safely while the shared integration remains restricted?
- OpenCode: Business owner reportCan we see and stop spending at the provider without access to the intermediary console?
- OpenCode: Technical manager reportIs any replacement key also reused by an unrelated production service?
- OpenCode: Software engineer reportDoes deleting the tool configuration actually invalidate the credential at its issuer?
- OpenCode: Customer service reportAre we reporting our own verified service status or repeating an unconfirmed external claim?
- OpenCode: Customer reportWhat is confirmed about my service, and what is still being investigated?
- 08Lightning AI Studio credential incidentCritical* · Vendor-confirmed incident
- Lightning AI: Evidence and scopeThe vendor’s total developer audience is not an affected-user count. A customer not yet identified as affected is not equivalent to a completed independent clearance.
- Lightning AI: Business impact and costsSuspension can stop development and production-related pipelines while exposed credentials may reach services outside the platform. Restoring the workspace and clearing downstream accounts are separate workstreams.
- Lightning AI: Technical exposure and controlsMap the Studio’s access to source repositories, cloud roles, model providers, databases and artifact stores. Include machine and service credentials beyond the user’s interactive login.
- Lightning AI: Response and recoveryResume the workflow after both the platform path and the connected-account remediation have documented acceptance.
- Lightning AI: Business manager reportAre we resuming a verified workflow or simply rerunning the last available environment?
- Lightning AI: Business owner reportCould the business recover its essential work if the development platform stayed unavailable?
- Lightning AI: Technical manager reportWhich identity still grants access outside the platform after the platform account is disabled?
- Lightning AI: Software engineer reportDoes this pipeline need every permission that the old shared workspace accumulated?
- Lightning AI: Customer service reportCan we tell the customer which function is available without making a claim about all connected systems?
- Lightning AI: Customer reportIs my service waiting on platform restoration, data validation or a separate security review?
- Cloud data and AI supply chainsRead the individual entries for impact, potential exposure, required actions and primary evidence. Operational priority depends on actual exposure.
- 09PingCAP / TiDB Cloud data exposureHigh · Vendor-confirmed exposure
- PingCAP: Evidence and scopeDo not convert the provider’s customer base into a victim count, or assume every customer had every information category exposed.
- PingCAP: Business impact and costsEven where production remains available, exposed query text or commercial metadata can create confidentiality and targeted-phishing concerns. Investigation needs the data owner’s interpretation of what those records mean, not only a database uptime check.
- PingCAP: Technical exposure and controlsMap what the business placed in database tooling, query text, support materials and commercial records. Separate production table contents from control-plane metadata and information copied into support workflows.
- PingCAP: Response and recoveryClose the business investigation only after customer-specific exposure questions and required account actions have an explicit, documented disposition.
- PingCAP: Business manager reportWhich records outside the production database could still matter to our customers?
- PingCAP: Business owner reportWhat evidence supports the scope of our statement to customers?
- PingCAP: Technical manager reportWhere are we treating a lack of logs as if it were evidence of no access?
- PingCAP: Software engineer reportCan the same fault be diagnosed without copying production records into a support ticket?
- PingCAP: Customer service reportAre we answering this customer’s question or only repeating the provider’s general notice?
- PingCAP: Customer reportDoes the notice distinguish confirmed exposure from information still under review?
- 10LiteLLM release compromise and revised recovery guidanceCritical* · Vendor and researcher confirmed
- LiteLLM: Evidence and scopeA clean source repository does not clear a distributed artifact. A deleted temporary marker does not prove that an environment was never exposed.
- LiteLLM: Business impact and costsThe incident can combine inference interruption with access to unrelated accounts reachable from the environment. Replacing a dependency without reviewing those accounts may restore service while leaving the wider problem unresolved.
- LiteLLM: Technical exposure and controlsRecord installation history, wheel origin, image digest, registry and execution evidence. Trace the permissions available to the environment, including provider keys, database access and cloud identity.
- LiteLLM: Response and recoveryResume gateway traffic only when the clean execution environment, downstream credentials and usage controls have been reviewed together.
- LiteLLM: Business manager reportWhich task genuinely requires immediate AI access, and which can wait for a clean path?
- LiteLLM: Business owner reportWhat other accounts could the gateway reach beyond its advertised AI-routing function?
- LiteLLM: Technical manager reportCan every team explain why its usual package inspection workflow may be unsafe here?
- LiteLLM: Software engineer reportDoes our verification start the very runtime we are trying to keep inactive?
- LiteLLM: Customer service reportWhat can we confirm about this customer’s service while the gateway investigation continues?
- LiteLLM: Customer reportIs the proposed workaround approved by the business operating my service?
- Device claims and legacy systemsRead the individual entries for impact, potential exposure, required actions and primary evidence. Operational priority depends on actual exposure.
- 11iPhone proximity-attack and Cellebrite claimsHigh* · Claim; partly corroborated
- iPhone: Evidence and scopeDo not claim all iPhones are compromised, a particular nearby-radio scenario is proven, or a specific customer was targeted based on a circulating thread.
- iPhone: Business impact and costsUnsupported devices and uncertainty about a trusted handset can disrupt both access and recovery if the same phone is the only approval factor. The business needs a safe support and replacement path without making unsupported attribution claims.
- iPhone: Technical exposure and controlsInventory supported devices and their update status. Assess targeted-risk indicators through the established mobile-security process, separately from general social-media claims.
- iPhone: Response and recoveryReturn a suspected device to sensitive use only under the responsible responder’s decision; routine patch completion alone is not forensic clearance.
- iPhone: Business manager reportCan essential approvals continue if one person’s phone is removed from use?
- iPhone: Business owner reportAre we responding to evidence about our staff or to an unverified general claim?
- iPhone: Technical manager reportWhat evidence do we lose if our help desk immediately wipes every suspicious device?
- iPhone: Software engineer reportCan the application revoke a suspect session without losing control of the user’s whole account?
- iPhone: Customer service reportIs this a routine update question or evidence requiring specialist assessment?
- iPhone: Customer reportIs the advice coming from the device vendor or a verified responder?
- 12Legacy PHP exposure: the “internet kill switch” claimCritical* · Overlapping PHP exposure
- legacy PHP: Evidence and scopeVersion-disclosing website samples cannot establish the number of affected people or predict a permanent failure of a fixed share of the internet.
- legacy PHP: Business impact and costsLegacy constraints can turn an urgent patch into a larger operational decision. The cost includes maintenance uncertainty, specialist availability and repeated emergency changes, as well as any eventual data and workflow migration.
- legacy PHP: Technical exposure and controlsFind the business function, maintainer, runtime and dependencies behind each legacy service. Determine whether a vendor provides a verifiable backport and what remains outside that support commitment.
- legacy PHP: Response and recoveryAccept a temporary fix only with an accountable owner, expiry or review point, and a funded route to sustainable support.
- legacy PHP: Business manager reportWhich custom feature is worth maintaining, and which merely keeps an old process alive?
- legacy PHP: Business owner reportWhat is the credible cost and operating consequence of remaining on this system for another year?
- legacy PHP: Technical manager reportWho will supply and validate the next security fix after this emergency backport?
- legacy PHP: Software engineer reportWhich hidden behavior will fail only after customers start using the replacement?
- legacy PHP: Customer service reportCan we answer an order question from before the migration without sending the customer elsewhere?
- legacy PHP: Customer reportWill my existing order and support rights continue through the platform change?
- AI operations and software assuranceRead the individual entries for impact, potential exposure, required actions and primary evidence. Operational priority depends on actual exposure.
- 13Symantec: autonomous LLMjacking and “Skynet”High · Honeypot observations
- LLMjacking: Evidence and scopeAttempted use, provider billing exposure and successful compromise are different outcomes. Keep them separate in incident and impact reporting.
- LLMjacking: Business impact and costsUnauthorised inference can consume budget or capacity without taking control of the application. A tool-connected service can have additional consequences if it accepts untrusted requests with privileged authority.
- LLMjacking: Technical exposure and controlsInventory every model endpoint, its authentication, network exposure, provider credential, resource limits and any tools it can invoke. Include temporary demonstrations and abandoned test deployments.
- LLMjacking: Response and recoveryExpose an AI service only when its owner can identify permitted users, bound resource use and interrupt abuse without depending on model cooperation.
- LLMjacking: Business manager reportWho would notice that a demonstration endpoint was still running next month?
- LLMjacking: Business owner reportWhat is the maximum business exposure before someone can stop this service?
- LLMjacking: Technical manager reportWhat happens when the budget service fails or an attacker distributes requests across many clients?
- LLMjacking: Software engineer reportCan a request spend money or invoke a tool before its authorisation and budget checks finish?
- LLMjacking: Customer service reportCan a customer still reach a person when the AI service has been deliberately restricted?
- LLMjacking: Customer reportIs this an approved service with a responsible operator and a clear privacy explanation?
- 14AI-generated code and application securityHigh* · Expert warning / case example
- AI-generated code: Evidence and scopeThe origin of code does not prove it secure or insecure. Passing tests that repeat the implementation’s assumptions is not independent evidence of correct authorisation.
- AI-generated code: Business impact and costsA feature can work correctly for its intended user while exposing another customer’s records. The business consequence depends on the reachable data and actions, not the size of the code change or the speed at which it was written.
- AI-generated code: Technical exposure and controlsIdentify security-sensitive changes and the trust boundaries they affect. Review object ownership, tenant separation, role checks, data export and the privileges available to the coding environment.
- AI-generated code: Response and recoveryRelease the feature only after an accountable reviewer accepts the security boundary and the negative tests exercise behavior beyond the happy path.
- AI-generated code: Business manager reportWhat must this feature refuse even when the user can guess another record’s identifier?
- AI-generated code: Business owner reportAre delivery targets rewarding speed while leaving nobody time to challenge the design?
- AI-generated code: Technical manager reportCould the same mistaken assumption have been copied into both the feature and its tests?
- AI-generated code: Software engineer reportWhat changes when I make the request directly instead of following the intended UI?
- AI-generated code: Customer service reportDoes this report describe a usability defect or access to information belonging to someone else?
- AI-generated code: Customer reportHow can I report this without collecting or sharing more of someone else’s information?
- Runtime and network controlsRead the individual entries for impact, potential exposure, required actions and primary evidence. Operational priority depends on actual exposure.
- 15Node.js October security releasesHigh · Confirmed; patches released
- Node.js: Evidence and scopeUpdating a developer workstation does not update deployed containers, server processes or embedded copies. Package-lock changes alone do not establish the running runtime version.
- Node.js: Business impact and costsRuntime changes can affect several business services at once. A shared base image reduces duplication but can also leave many workloads on the same outdated dependency if rollout ownership is unclear.
- Node.js: Technical exposure and controlsInventory running Node versions and image origins across application servers, scheduled jobs, CI runners and managed hosting. Determine which team controls each deployment and its restart process.
- Node.js: Response and recoveryComplete remediation when the deployed fleet has verified coverage or time-bounded owned exceptions, and critical integration tests pass.
- Node.js: Business manager reportWhich delayed or overnight workflow could fail after the visible application looks healthy?
- Node.js: Business owner reportWhat recurring operating cost comes from services that cannot be updated routinely?
- Node.js: Technical manager reportAre we measuring what is deployed or only what developers intended to deploy?
- Node.js: Software engineer reportCould a background job or old process continue using the previous runtime after the rollout?
- Node.js: Customer service reportIs this a known service regression or a new account-security concern?
- Node.js: Customer reportWhat action is actually needed from me, rather than from the service operator?
- 16NSA reminder: Cisco Smart Install exposureHigh* · Established configuration risk
- Cisco: Evidence and scopeA device inventory or reachable feature does not prove configuration theft or compromise. Configuration risk and vulnerability-specific patching require separate checks.
- Cisco: Business impact and costsNetwork disruption can stop several operational systems simultaneously. A leaked configuration may reveal topology or credentials, so the response can extend beyond restoring connectivity.
- Cisco: Technical exposure and controlsIdentify affected network devices, whether Smart Install is required, who can reach management interfaces and how configuration backups and administrative credentials are protected.
- Cisco: Response and recoveryAccept the change when management exposure is controlled and the business can recover a device without recreating the same unsafe access path.
- Cisco: Business manager reportCan the warehouse continue essential work if the network change needs recovery?
- Cisco: Business owner reportWhich business location relies on equipment nobody can confidently maintain or recover?
- Cisco: Technical manager reportWill the control change also cut off the authorised team’s recovery path?
- Cisco: Software engineer reportDoes a brief site outage cause duplicated transactions when connectivity returns?
- Cisco: Customer service reportWhich customer requests require reconciliation after the connection returns?
- Cisco: Customer reportWas my request completed before the connection failed?
- Cloud platform incidentsRead the individual entries for impact, potential exposure, required actions and primary evidence. Operational priority depends on actual exposure.
- 17Railway customer secrets exposureCritical · Vendor notice; scope under review
- Railway: Evidence and scopeKeep confirmed account exposure, precautionary rotation and the provider’s wider campaign hypotheses separate. The disclosure does not establish that all Railway customers were compromised.
- Railway: Business impact and costsA platform incident can create several simultaneous investigations because the secrets stored there unlock other accounts. The business needs a continuity decision for each connection, rather than a single declaration that the application is back online.
- Railway: Technical exposure and controlsInventory variable names and their permission scope without copying secret values into the incident register. Trace each credential to its issuing service, owner, consumers and available usage history.
- Railway: Response and recoveryResume each integration when its owner can show a trusted execution path, controlled credentials and an explicit decision on unresolved account activity.
- Railway: Business manager reportWhich restored workflow still depends on an account whose access has not been checked?
- Railway: Business owner reportHow much of the company could one environment configuration authorize?
- Railway: Technical manager reportCan we prove the old credential stopped working everywhere it was accepted?
- Railway: Software engineer reportWhich infrequent job will fail tomorrow because it still uses yesterday’s secret?
- Railway: Customer service reportAre we promising an investigation outcome merely because the website loads again?
- Railway: Customer reportWhat has the business established about my account rather than its hosting provider generally?
- 18Zeabur compromise and announced service shutdownCritical · Vendor-confirmed intrusion
- Zeabur: Evidence and scopeDo not apply a finding from one infrastructure category to every tenant. A migration deadline does not settle whether exported data or credentials are trustworthy.
- Zeabur: Business impact and costsInvestigation competes with a fixed exit timetable. Rushed migration can lose orders, miss background processes or carry compromised credentials into the replacement. Continuity planning must budget for both clean rebuilding and data reconciliation.
- Zeabur: Technical exposure and controlsMap each service to its hosting category and incident evidence. Identify data exports, credentials, deployment definitions, domains and scheduled tasks needed to recreate the business workflow independently.
- Zeabur: Response and recoveryApprove exit only when the replacement supports essential operations, the data exceptions are understood and the business can operate without the departing provider.
- Zeabur: Business manager reportWhat work occurs outside the visible application that the replacement must still perform?
- Zeabur: Business owner reportCan we continue trading if the old provider becomes unavailable before our preferred migration date?
- Zeabur: Technical manager reportWhich assumption about the old platform would prevent us from rebuilding independently?
- Zeabur: Software engineer reportWhat would we need to reconstruct this service if the old control panel disappeared now?
- Zeabur: Customer service reportCan we resolve an old order after the hosting account is closed?
- Zeabur: Customer reportHow will the business preserve my open order or support request through the move?
- Compromised official releasesRead the individual entries for impact, potential exposure, required actions and primary evidence. Operational priority depends on actual exposure.
- 19OVHcloud CLI malicious release binariesCritical · Vendor-confirmed artifact replacement
- OVHcloud: Evidence and scopeA trusted download location and a clean source tree do not independently establish that a particular downloaded binary was safe.
- OVHcloud: Business impact and costsAn administrative workstation can connect a narrow software distribution incident to several business systems. Recovery needs to address the workstation and reachable accounts, while preserving an alternative way to operate production.
- OVHcloud: Technical exposure and controlsLocate downloaded binaries, their identifiers, acquisition times and execution hosts. Map the local files and identities available to those processes, including credentials for services unrelated to the CLI vendor.
- OVHcloud: Response and recoveryReturn administrative access only when the host, tooling and relevant account controls have each passed their own verification checks.
- OVHcloud: Business manager reportWhich business operation depends on the workstation we have just isolated?
- OVHcloud: Business owner reportHow many critical services can a single developer laptop administer?
- OVHcloud: Technical manager reportAre we following where the binary ran or merely which cloud service it was meant to manage?
- OVHcloud: Software engineer reportWhat independent evidence supports the replacement artifact we are about to trust?
- OVHcloud: Customer service reportDoes our statement describe evidence about this service or a general software advisory?
- OVHcloud: Customer reportWhat action, if any, is justified by the facts established about my account?
- 20Rank Math PRO malicious plugin distributionCritical · Vendor-confirmed package compromise
- Rank Math: Evidence and scopeDo not equate all Rank Math installations with affected sites, or assume a clean replacement plugin removes changes already made elsewhere on a site.
- Rank Math: Business impact and costsA site can keep selling while its integrity is uncertain. Restoring an earlier database can also erase legitimate orders or support activity, so recovery must reconcile security with the business transactions created after the trusted backup.
- Rank Math: Technical exposure and controlsEstablish the installed edition, artifact timing and activation evidence. Review site files, database changes, administrator accounts and the authority available to the web application.
- Rank Math: Response and recoveryReopen normal publishing or trading only after both technical integrity and business-record reconciliation have been accepted by their owners.
- Rank Math: Business manager reportWhich genuine customer actions will an older backup erase?
- Rank Math: Business owner reportWhich maintenance responsibilities would a migration remove, and which would remain with us?
- Rank Math: Technical manager reportWhat could remain in the database after the plugin files have been replaced?
- Rank Math: Software engineer reportHow will we recover valid recent orders without restoring malicious state alongside them?
- Rank Math: Customer service reportCan we verify this order without asking the customer to send full payment details?
- Rank Math: Customer reportWhat has the store verified about my transaction and any information involved?
- Website management and cloud backupRead the individual entries for impact, potential exposure, required actions and primary evidence. Operational priority depends on actual exposure.
- 21TeamUpdraft customer data and connected site accessCritical* · Vendor notice; connected-site abuse
- TeamUpdraft: Evidence and scopeInstallation totals are not a confirmed victim count. Distinguish vendor information exposure, connected-site access and evidence of changes on a particular site.
- TeamUpdraft: Business impact and costsA recovery service may become part of the incident rather than an independent escape route. The business may need to verify both production integrity and backup usability before it can rely on restoration.
- TeamUpdraft: Technical exposure and controlsMap every site connected to management services, including forgotten registrations. Review the permissions of those relationships, recent account changes, plugin activity and the trustworthiness of available backups.
- TeamUpdraft: Response and recoveryAccept recovery when the production site and the management and backup paths have independently verified access and integrity.
- TeamUpdraft: Business manager reportCan the team complete real work from the backup we are relying on?
- TeamUpdraft: Business owner reportWhat remains available if our central website management account cannot be trusted?
- TeamUpdraft: Technical manager reportWhich old connection still has authority that nobody actively manages?
- TeamUpdraft: Software engineer reportDoes the backup contain the same unauthorized account we are trying to remove?
- TeamUpdraft: Customer service reportAre we treating a restored page as proof that all account records are correct?
- TeamUpdraft: Customer reportWhat verified information can the business provide about the records relevant to me?
- 22ConnectWise Cloud Backup and AI accelerated identity abuseCritical · Vendor-confirmed identity incident
- ConnectWise: Evidence and scopeAn application’s presence or a sign-in record is not by itself proof of data exfiltration. Do not generalize this event to all Microsoft tenants or declare a tenant clear from supplier uptime.
- ConnectWise: Business impact and costsA trusted backup integration can expose business information without interrupting ordinary user login. Disabling it may also reduce recovery coverage, so the business needs a temporary continuity decision while identity scope is investigated.
- ConnectWise: Technical exposure and controlsMap enterprise applications, service principals, owners, credentials, consent grants and roles. Relate app-only activity to the mailboxes, files and other resources that the granted permissions could reach.
- ConnectWise: Response and recoveryRe-enable the integration only after identity ownership, required permissions, account-specific findings and the independent recovery plan have been approved.
- ConnectWise: Business manager reportWhat business work is being created while our normal backup integration is restricted?
- ConnectWise: Business owner reportCan the business recover if its backup identity is part of the incident?
- ConnectWise: Technical manager reportWhich permissions remain usable after every human user has changed their password?
- ConnectWise: Software engineer reportCan this application access a resource that its business purpose does not require?
- ConnectWise: Customer service reportDoes our answer distinguish possible access from verified activity involving this customer?
- ConnectWise: Customer reportWhat does the business know about my information, and what remains under investigation?
- Compromised npm packagesRead the individual entries for impact, potential exposure, required actions and primary evidence. Operational priority depends on actual exposure.
- 23Tensorlake malicious npm packagesCritical · Maintainer-confirmed malware
- Tensorlake: Evidence and scopePackage installation can matter even without ordinary SDK use. Follow the maintainer’s containment and neutralization sequence before revoking a token that the destructive service monitors.
- Tensorlake: Business impact and costsA package event can interrupt development and create a destructive-recovery hazard. Teams need clean capacity to continue essential work while responders preserve evidence and prevent credential changes from triggering further damage.
- Tensorlake: Technical exposure and controlsTrace exact package versions and installation activity through lockfiles, registry records and CI history. Map execution environments and accessible credentials, including transitive installation paths.
- Tensorlake: Response and recoveryResume development or release work only after the environment, credential recovery sequence and package publishing authority have been reviewed together.
- Tensorlake: Business manager reportCould an uncoordinated recovery action make the business interruption worse?
- Tensorlake: Business owner reportAre teams following the documented incident conditions or a generic speed target?
- Tensorlake: Technical manager reportWho can confirm it is safe to revoke the monitored token?
- Tensorlake: Software engineer reportWhat code runs during installation before our application ever imports the SDK?
- Tensorlake: Customer service reportAre we promising a release before its build environment has been cleared for use?
- Tensorlake: Customer reportHas the supplier established an effect on my product version or only on its internal tooling?
- 24SubQuery backdoored npm dependencyCritical · Independent technical analysis
- SubQuery: Evidence and scopeA registry download count is not a count of compromised organizations. A valid artifact hash proves identity against that reference, not that the referenced contents are safe.
- SubQuery: Business impact and costsA dependency introduced for one feature may reach authority used to publish unrelated software. The business needs to distinguish affected development environments from released products and investigate whether the release process itself was used.
- SubQuery: Technical exposure and controlsUse lockfiles and build evidence to identify exact artifacts and transitive paths. Establish where installation or execution occurred and which repository, publishing, cloud or service credentials were available there.
- SubQuery: Response and recoveryAuthorize releases only when the build environment, publishing identity and resulting artifacts have sufficient evidence of integrity.
- SubQuery: Business manager reportWhich customer commitment depends on a pipeline whose integrity is still unresolved?
- SubQuery: Business owner reportWhat evidence would let us confidently distribute a new version after this incident?
- SubQuery: Technical manager reportWhere could the same dependency run outside the application repository we first checked?
- SubQuery: Software engineer reportDoes our verification test the package contents or only the label attached to them?
- SubQuery: Customer service reportCan we identify the product version this customer actually obtained?
- SubQuery: Customer reportIs this advice tied to my installed product or to a general package warning?
- Repository access and certificate remediationRead the individual entries for impact, potential exposure, required actions and primary evidence. Operational priority depends on actual exposure.
- 25GhostAction malicious GitHub workflowsCritical* · Research-observed ongoing campaign
- GhostAction: Evidence and scopeA clean application diff does not clear CI configuration. Masked logs and trusted action pins do not by themselves prevent a malicious first-party workflow from using available secrets.
- GhostAction: Business impact and costsA small configuration change may turn routine CI into a route to production or publishing authority. The business can face a release freeze and cross-account review even if the application continues to behave normally.
- GhostAction: Technical exposure and controlsReview workflow definitions, triggering events, repository permissions and changes to automation identities. Map secrets and short-lived credentials to the jobs able to request them and the environments they can affect.
- GhostAction: Response and recoveryResume automated publishing when workflow integrity, identity ownership and deployment authorization have been reviewed together.
- GhostAction: Business manager reportWho is allowed to approve a production change while normal automation is restricted?
- GhostAction: Business owner reportDoes someone with routine repository access also hold an unreviewed route to production?
- GhostAction: Technical manager reportWhich workflow can request production authority from an event we do not sufficiently control?
- GhostAction: Software engineer reportCan a change to this workflow bypass the review that protects application code?
- GhostAction: Customer service reportAre we distinguishing a delayed release from a confirmed issue in a customer’s installed version?
- GhostAction: Customer reportHas the supplier verified the integrity of the release I received?
- 26Tailscale response to the eMudhra certificate incidentHigh · Vendor advisory; related exposure
- Tailscale: Evidence and scopeDo not merge certificate trust, control-plane communication and encrypted node-to-node traffic into one claim. A connected VPN icon does not establish that the client has the required trust update.
- Tailscale: Business impact and costsUpdating a security dependency can disrupt remote work if it is not coordinated, while delaying the update leaves the stated trust concern unresolved. The business needs verified client coverage and an independent recovery route for critical administration.
- Tailscale: Technical exposure and controlsInventory active Tailscale clients, versions and installation paths, including servers and infrequently used devices. Identify how teams will retain administrative access while validating the required update.
- Tailscale: Response and recoveryClose the rollout when required devices are verified on the approved client and remaining exceptions have an explicit, time-bounded operating decision.
- Tailscale: Business manager reportWhich rarely used device becomes critical when we need emergency access?
- Tailscale: Business owner reportCan we maintain the business if the normal remote administration path needs urgent repair?
- Tailscale: Technical manager reportWhich device reports a completed install while still running an older client?
- Tailscale: Software engineer reportDoes this test prove the intended client is running or only that some network path works?
- Tailscale: Customer service reportAre we explaining the vendor’s actual scope or repeating an exaggerated headline?
- Tailscale: Customer reportIs the proposed workaround preserving the security checks the update is intended to restore?
- Additional research and critical patchesRead the individual entries for impact, potential exposure, required actions and primary evidence. Operational priority depends on actual exposure.
- 27AOMEI update delivery compromiseCritical* · Google threat investigation
- 28GitLab critical server vulnerability and security patchesCritical* · Vendor security release
Response
- Response prioritiesThe operational overlap is shared access: credentials, release pipelines, certificate trust and recovery systems connect otherwise separate events. The following priorities are editorial recommendations for an exposed bu
- Actions for the first dayThe operational overlap is shared access: credentials, release pipelines, certificate trust and recovery systems connect otherwise separate events. The following priorities are editorial recommendations for an exposed bu
- Contain and preserveContain and preserve. Assign an incident lead. Isolate confirmed compromised execution environments, disable affected integrations where advised, and retain logs and artifact hashes. Follow product-specific sequencing: T
- Patch reachable systemsPatch reachable systems. Inventory actual PHP, Node.js and GitLab versions, including appliances and images. Verify deployed fixes rather than only package files. Apply certificate distrust through the verifier each appl
- Follow credentials downstreamFollow credentials downstream. Review every system a stolen key or application identity could reach. Rotate from clean systems after containing paths that can read replacement secrets. Check identity changes and retained
- Recovery and evidence limitsResponse
- Recovery and migration decisionsResponse
- Test independent recoveryTest independent recovery. Confirm clean backup versions, separate recovery credentials and a demonstrated restore. Keep supplier restoration status separate from downstream tenant or endpoint clearance. ConnectWise repo
- Plan the exit before cutoverPlan the exit before cutover. For Zeabur, set an internal migration date ahead of December service restrictions. Reconcile records, preserve assets and dependencies, rotate exposed credentials, test restore and rollback,
- Select controls and accountabilitySelect controls and accountability. Evaluate any replacement platform against patch ownership, scoped identities, audit-log access, tested recovery, supplier response and exit options. Moving to a managed platform can re
- Counting and evidence limitsThe report contains 28 topics, not 28 independent breaches. Legacy PHP (12) overlaps PHP (01); Tailscale (26) is downstream remediation of eMudhra (06); iPhone item 11 remains a qualified watch item. The companion articl
Digital Younger Dryas
- The Digital Younger DryasA growing business can have capable people, useful products and modern technology, yet still be vulnerable to a sudden change in the systems it depends on. The next advantage may be the ability to keep trading while thos
- Preserve your optionsKeep the ability to trade, recover and change direction when normal access, suppliers or software can no longer be relied on.
- A change in conditions can overturn a good operating model.I use Digital Younger Dryas to describe a scenario in which several assumptions supporting digital growth become unreliable at the same time. Software distribution needs investigation. Credentials must be withdrawn. A su
- Three signals of shared exposureThe Cyberpolycrisis network map groups 26 topics into 23 baseline themes. It describes shared exposures, not a single campaign. Three examples show why a technology leader should look beyond individual incident tickets.T
- A familiar package can become a route into connected accounts.JFrog documented credential-stealing payloads in LiteLLM 1.107.0 wheels and an affected official Docker image. The source archive did not contain the same payload files. That distinction makes the installed artifact, and
- Trust changes can travel through the application stack.The Node.js security release of 21 October 2026 explicitly includes certificate updates addressing the eMudhra intermediate CA compromise. A certificate incident can therefore require work in runtimes and deployed applic
- Recovery can become another dependency.Google’s London incident report attributes the October disruption to a power event in europe-west2-b, with effects on regional services. The report does not establish a cyberattack. It illustrates how availability proble
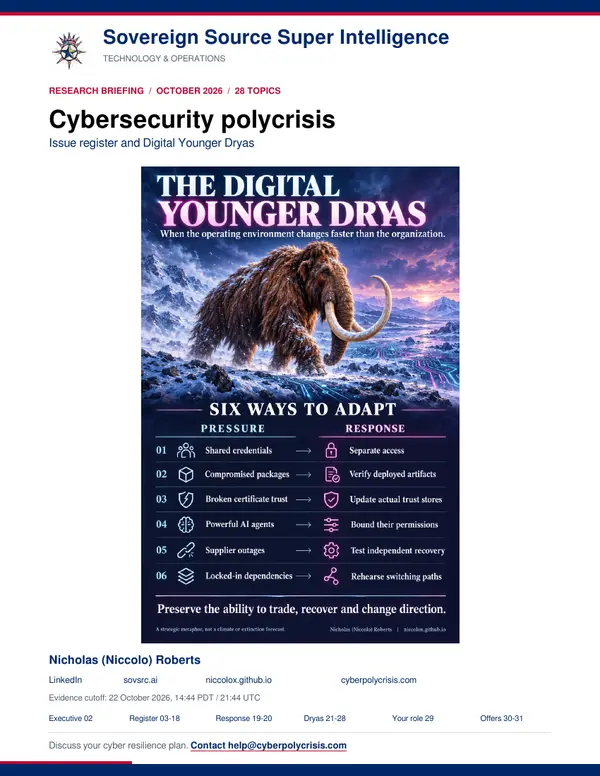
- Six adaptations for resilienceFor a medium-sized business pursuing growth, the practical aim is to preserve useful capacity without creating an unmanageable estate. These six responses are the text version of the infographic.
- Separate access.Give production, development, suppliers and AI agents distinct identities with narrow permissions. Keep an owner and revocation path for each important integration. Shared administrative credentials make otherwise separa
- Verify deployed artifacts.Record what was installed, where it came from and which workload uses it. Retain known-good build inputs and a clean rebuilding path. Review source and distribution evidence together; a familiar name or signed release al
- Update actual trust stores.Identify whether each service relies on operating-system, runtime or bundled certificate authorities. Assign remediation to the right owner and verify the application after restart or redeployment. Keep certificate check
- Bound their permissions.Match tool access, data visibility and spending authority to the task. Require approval for consequential actions and retain useful logs. A well-written instruction is valuable, but permissions and application controls m
- Test independent recovery.Protect backup access and recovery procedures from the same failure that affects production. Decide which services must continue, which can pause and how customers will be informed. A documented fallback earns confidence
- Rehearse switching paths.Know how to export essential data, replace an integration and terminate delegated access. Choose alternatives where their business value justifies the cost. More suppliers can add complexity; the useful measure is whethe
- Recovery and switching pathsBound agent permissions, test independent recovery and rehearse switching paths. These are adaptations four through six in the report.
- A retailer loses its operating pathThis is a tabletop scenario for a growing commerce business. It is not a claim about a particular company or a documented chain linking the incidents above.A retailer discovers that a development dependency may have expo
- Access becomes suspectThis stage belongs to the retailer tabletop exercise. It is an illustrative sequence, not an observed attack chain.A retailer discovers that a development dependency may have exposed credentials used by its commerce inte
- Containment limits automationThis stage belongs to the retailer tabletop exercise. It is an illustrative sequence, not an observed attack chain.The impact comes from the interaction: accepting orders creates commitments while fulfillment visibility
- Customer commitments need a fallbackThis stage belongs to the retailer tabletop exercise. It is an illustrative sequence, not an observed attack chain.The impact comes from the interaction: accepting orders creates commitments while fulfillment visibility
- A practical 30 day planUse this as a starting sequence, adjusted for the business’s exposure and existing controls. Active compromise takes priority over the calendar.Growth needs room to adapt. A business that can contain a compromise, restor
- Week 1: map the customer promise.Select the workflows that protect revenue and customer trust. Map their systems, identities, software inputs, suppliers and recovery owners. Agree the tolerable interruption and data loss for each workflow.Deliverable: a
- Week 2: remove avoidable shared exposure.Separate broadly shared identities, reduce agent permissions and address exposed or unsupported software. Verify relevant runtime and trust updates. Use incident-specific response instructions where compromise is suspect
- Week 3: rehearse a difficult recovery.Run the retailer scenario against one real workflow. Remove a normal supplier or identity path from the exercise. Restore from verified inputs, account for missing or duplicated transactions, and test customer communicat
- Week 4: turn findings into operating decisions.Fund the changes that remove the largest obstacles to continuity. Confirm supplier exit requirements and the cost of maintaining alternatives. Make the next exercise someone’s responsibility and keep the recovery evidenc
- Six ways to adaptAn original AI-generated illustration of operational adaptation. The Digital Younger Dryas is a strategic metaphor, not a claim that a climate event caused a single mammoth extinction or a prediction of inevitable digita
- Companion articlesThe Digital Younger Dryas belongs to a series on how separate technology failures can place simultaneous demands on a business. These companion articles provide the incident and dependency context for the operating exerc
- The Cybersecurity PolycrisisEight case studies examine application vulnerabilities, cloud availability, AI-assisted intrusion, procurement policy, agent permissions, certificate trust and exposed provider credentials. The article separates document
- Cyberpolycrisis network mapThe network analysis connects shared dependencies across credentials, software delivery, AI tooling, certificate trust, service providers and recovery. Its 26-topic edition groups overlapping entries into 23 baseline the
- Using the articles with this reportUse the updated 28-topic register for the report's dated incident evidence and required actions. Use the network map to identify shared dependencies, then apply the Digital Younger Dryas exercises to a real customer work
Your role
- What this means for youThe same disruption creates different responsibilities. These four perspectives connect the report’s response priorities with business continuity and customer trust.
- Business ownerYour exposure is measured in interrupted sales, recovery costs and customer commitments you may struggle to keep. Identify the workflows that protect revenue, agree how much interruption and data loss the business can to
- Technology managerYour task is to turn a list of incidents into an owned, prioritized operating plan. Map critical services, suppliers, identities and integrations; establish actual exposure; and coordinate containment, patching and recov
- EngineerYour priority is to establish what ran, what it could access and what can now be trusted. Preserve logs and artifact hashes, verify deployed versions and dependency provenance, and follow incident-specific containment an
- CustomerYou experience resilience through a checkout that works, accurate order information, reliable delivery and support that can resolve exceptions. During a disruption, you need clear updates about service availability, whet
Migration offers
- Migration offersMagento to Shopify and WooCommerce to Shopify. AI-accelerated migration to de-risk and grow, with reviewed data mappings, tested integrations and a rehearsed transition.
- Magento to ShopifyWhen Magento upgrades, PHP patching and extension maintenance consume your delivery budget, growth work waits. Move to Shopify or Shopify Plus with a plan for your data, integrations and trading operations, so your team
- Move data with evidenceMove data with evidence. Map orders, customers, products, images and metadata. Reconcile historical totals and relationships; map custom attributes to Shopify metafields.Shopify operates the core platform and hosting. Yo
- Preserve the buying journeyPreserve the buying journey. Rebuild storefront and checkout workflows, plan customer account access, and validate discounts, redirects, SEO metadata and analytics.Shopify operates the core platform and hosting. Your tea
- Connect the operationConnect the operation. Design and test ERP, warehouse, finance, shipping and marketing integrations. Assess custom selling models before choosing apps or development work.Shopify operates the core platform and hosting. Y
- Rehearse the transitionRehearse the transition. Plan final order and stock updates, acceptance checks, launch responsibilities, recovery decisions, training and support.Shopify operates the core platform and hosting. Your team remains responsi
- AI-assisted, reviewed deliveryAI-assisted, reviewed delivery. Use AI to accelerate mapping, transformation scripts and test preparation, with human review and repeatable checks. Agree scope, fees and timing after assessing versions, extensions and bu
- WooCommerce to ShopifyWhen WordPress updates, plugin conflicts and checkout maintenance compete with selling, your team pays in time and delayed improvements. Move your commerce operation to Shopify with a plan for the workflows customers rel
- Move the store and its historyMove the store and its history. Map products, variations, images, customers, consent, orders and custom fields. Reconcile totals, associations and inventory before launch.Shopify operates the core platform and hosting. Y
- Replace business behavior thoughtfullyReplace business behavior thoughtfully. Assess subscriptions, memberships, bundles, reviews and custom pricing. Review payment provider eligibility before planning recurring billing changes.Shopify operates the core plat
- Plan content and connectionsPlan content and connections. Map pages, metadata and redirects; decide what stays on WordPress and who maintains it. Test fulfillment, refunds and connected systems.Shopify operates the core platform and hosting. Your t
- Launch with a runbookLaunch with a runbook. Rehearse checkout, analytics, open orders, returns and final stock updates. Define acceptance checks, recovery decisions, training and support.Shopify operates the core platform and hosting. Your t
- AI-assisted, reviewed deliveryAI-assisted, reviewed delivery. Accelerate mapping, transformation scripts and test preparation with reviewed outputs. Agree customer data and tool access, scope, fees and timing after assessing the plugin inventory and
- Experience at scaleNicholas (Niccolo) RobertsAt Digital Beverage Group, I led the move from Offset Figure to Shopify Plus and Linnworks, including 2 million historical orders representing $150 million in historical order value.
No matching sections. Try a product name, a risk or an action.